Report claims Kaspersky faked malware to trip up competitors’ products

Two former employees of Kaspersky Lab have accused the malware protection software company of seeding competitors’ products with fake malware signatures intended to make them erroneously label benign files on customers’ computers as malicious. The allegations, made in a report published by Reuters Friday morning, have been strongly denied by a Kaspersky Lab spokesperson.

According to Reuters, the “junk” files were tailored to have the same signature as legitimate files, based on the fingerprinting mechanisms of competitors’ products. To do this, the two former employees alleged, Kaspersky assigned employees to reverse-engineer competitors’ products to see how they identified malware and then tailored samples that would match the signatures of common, harmless files.

The report does not include many specifics about the alleged faked signatures, such as which files were targeted for identification as false positives.

Read 5 remaining paragraphs | Comments
People in rough neighborhoods trade HIV meds instead of taking them

The social environment of an area, including factors such as poverty, stress, and living conditions, contributes to the disease burden. A recent study published in AJPH shows that patients from a disordered environment don’t stick to their medication schedule, even for a potentially lethal condition like HIV. As the researchers found, residents of highly disordered neighborhoods will sell or trade their antiviral medication rather than taking it and adhering to their drug plans.

Poverty, a condition often associated with specific geographic regions or neighborhoods, is linked to many poor health outcomes. People living in poverty often lack access to nutritious food, good healthcare, strong social support, and other structural advantages that can ensure better health. Neighborhood disorder theory focuses on the role of economic disadvantage as a driver of adverse health outcomes among residents of poor neighborhoods. In previous studies, neighborhood disorder has been linked to increased HIV risk-taking behavior, which helps explain why HIV infections tend to cluster in areas with higher poverty and other forms of risk taking.

For this study, researchers interviewed 503 socioeconomically disadvantaged HIV-positive substance users, approximately half of whom were selling or trading their antiviral medication to other HIV positive individuals who didn’t have access to regular antiviral medication. Participants were from neighborhoods in urban Miami that have high and persistent levels of both HIV infections and poverty. Additionally, environmental risk factors were examined for these neighborhoods, such as prevalence of HIV and poverty levels.

Read 5 remaining paragraphs | Comments

Netflix shuts down its last data center, but it still runs a big IT operation

Netflix has been shifting technology from in-house data centers to third-party facilities for years now, and it says that the process is coming to its logical conclusion—the company is shutting down the last of its data centers.

Netflix still operates a huge IT infrastructure, but it’s located in Amazon’s cloud data centers, the facilities of Internet service providers, and Internet exchange points where many companies exchange traffic.

In an article titled “Netflix to pull plug on final data center,” The Wall Street Journal’s CIO Journal blog reported yesterday:

Read 6 remaining paragraphs | Comments

Lager-brewing yeast was probably born twice

Guinness stout and Bud Lite differ in, to be conservative, several ways, but one is that they’re brewed with very different types of yeast. Lager isn’t just a beer style, it’s a yeast lifestyle. Humans have been brewing with ale yeast—Saccharomyces cerevisiae—for thousands of years. But it was less than 600 years ago that European brewers stumbled on lager yeast, which behaves very differently and produces that distinctive lager flavor.

Lager yeast is a cross of ale yeast with another species, but it took until 2011 for that other species to finally be identified in Patagonian forests. A new study led by University of Wisconsin-Madison researchers EmilyClare Baker and Bing Wang presents the genome of this recently discovered parent, Saccharomyces eubayanus.

By comparing the genome with the two strains of lager yeast around today, the researchers may have settled a dispute about the biological origins of lager yeast. Looking at the two strains, there are many more differences between the ale yeast portions of their genomes than have accumulated in the Saccharomyces eubayanus portions. This points to independent hybridization events starting with different ale yeast parents rather than a single hybrid that has since split into two strains.

Read 2 remaining paragraphs | Comments

Rosetta follows Comet 67P through closest approach to the Sun

Thursday, the ESA’s Rosetta probe returned images from the comet it orbits during its closest approach to the Sun, or perihelion. At perihelion, Comet 67P/Churyumov–Gerasimenko is about 186 million kilometers from the Sun, or a bit outside of Earth’s orbit (150 million kilometers).

With the added warming from the Sun, the comet has been experiencing higher levels of activity, with gasses escaping from its interior at higher levels, pushing dust and other material out into space. Rosetta’s instruments indicate about 300 liters of water are being ejected every second, meaning the comet is losing 26 million kilograms per day during this period. Another 86 million kilograms of dust are also being lost. The activity should remain high for several weeks after perihelion.

Because of the large volumes of material jetting out of the comet, the ESA’s operators have backed Rosetta off to an orbit that’s over 325km from the comet’s surface. But that’s still close enough for some pretty spectacular images.

Read on Ars Technica | Comments

Gallery: A practical, low-tech Japan

When I was growing up, I was always told that we have so much to learn from Japan. I grew up during the rise of the Japanese auto industry, I was taught “Japanese” business tactics, and I watched movies like Gung Ho that portrayed discipline, perseverance, and efficiency.

On my first trip to Japan, though, I wanted to explore the weird and wacky high-tech world the media has portrayed so often. What I found was a place that isn’t as “high tech” as many westerners assume but rather a relatively “low tech” cornucopia of conveniences that could make many westerners jealous.

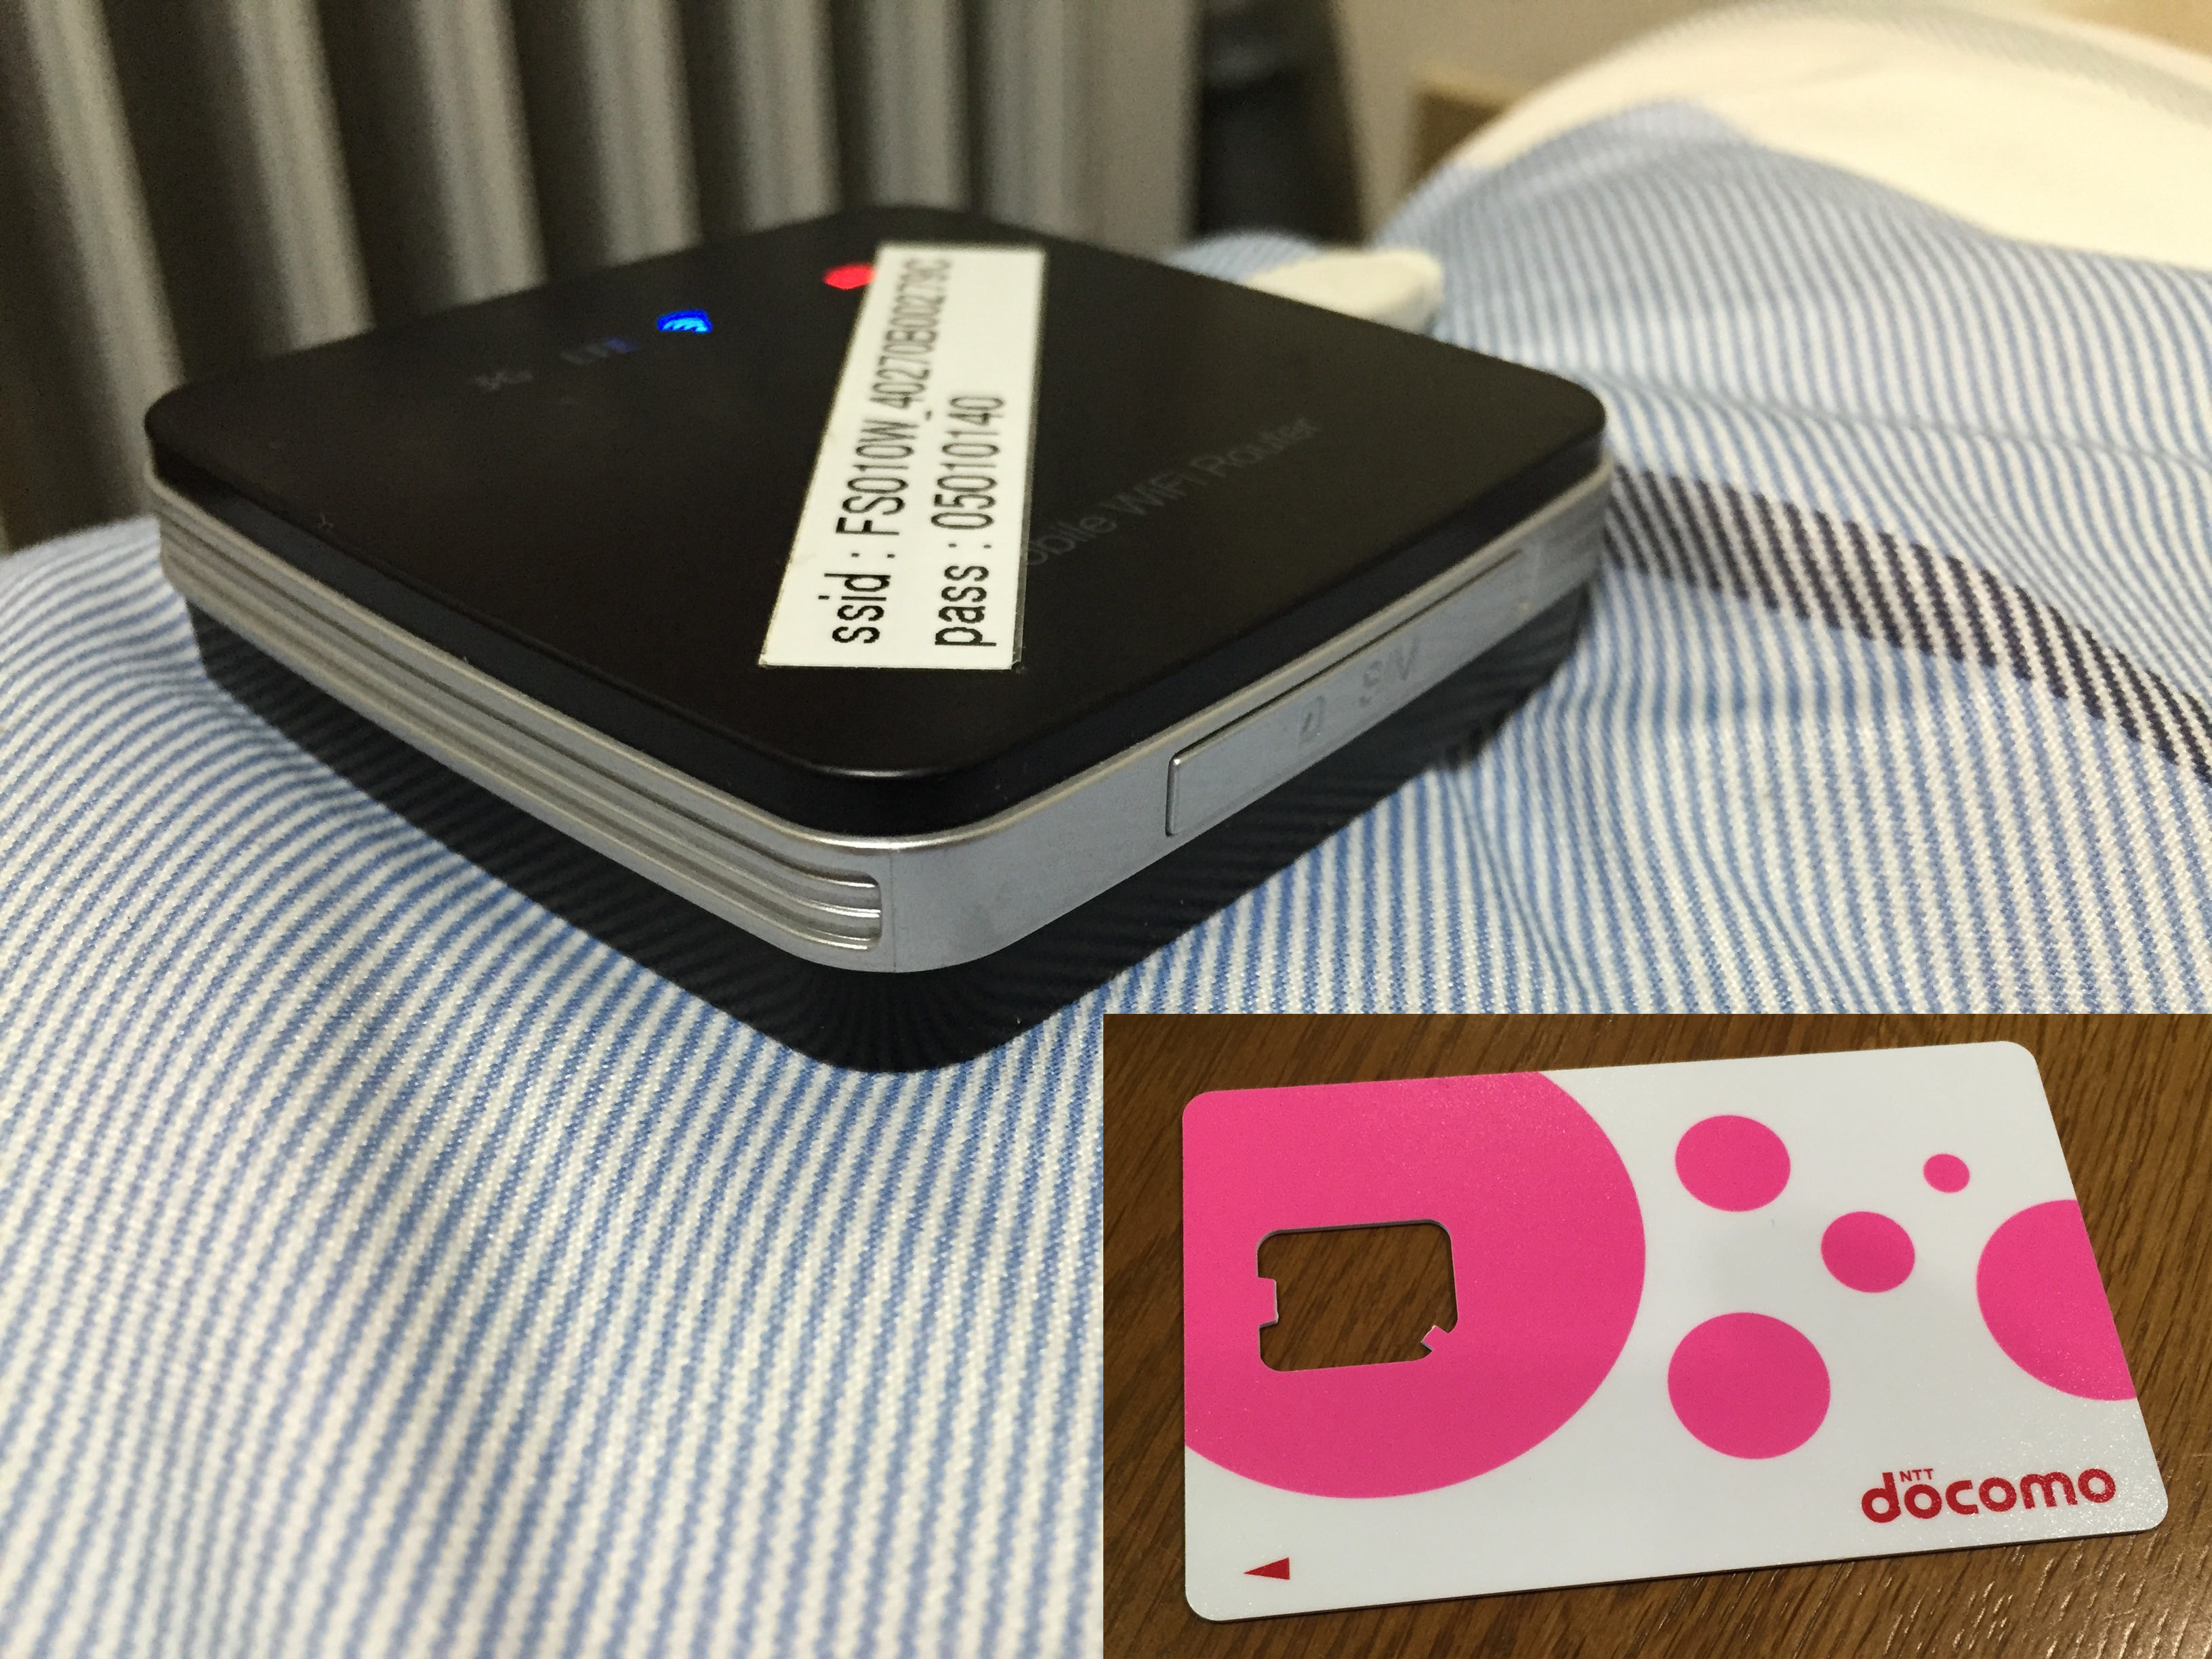
The first thing I noticed was the lack of “open” Wi-Fi before leaving for Japan. My research found that in most places, free Wi-Fi had to be registered for before entering Japan; it’s not ubiquitous. Despite the airports or an occasional restaurant or tourist site offering free Wi-Fi, I found this to be true. Luckily, my Airbnb provided me with a free mobile access point, and my $13 sim for my unlocked Blu Android phone filled in the gaps.

Read 3 remaining paragraphs | Comments

Politicians can only view secret trade pact in special viewing room

The fact that most people have still never heard of the world’s biggest trade deal—the Transatlantic Trade and Investment Partnership (TTIP) between the US and Europe—even after two years of negotiations, might suggest that whatever its problems, maintaining secrecy is not one of them. But the European Commission begs to differ: since the end of July, instead of sending up-to-the-minute summaries of its talks with the US to EU politicians, the Commission now requires that national politicians travel all the way to Brussels to a special reading room where the texts can be viewed under tight security. MEPs must also use this same system.

The EC made this rather drastic move in response to confidential TTIP documents appearing on the non-profit investigative news site Correct!v. News of this secret reading room was revealed in a confidential report of an EU meeting that took place on 24 July… which rather embarrassingly was then also leaked to the same site.

The new system is pretty insulting for top politicians, who are not used to being treated likely naughty schoolchildren that require constant adult supervision. Furthermore, considering the wide-ranging implications of TTIP, you’d think that the EC would want to make it easier for European politicians to read the latest documents, so that they know what is being negotiated in their name.

Read 7 remaining paragraphs | Comments

OwnStar Wi-Fi attack now grabs BMW, Mercedes, and Chrysler cars’ virtual keys

Remember OwnStar? Earlier this month, security researcher and NSA Playset contributor Samy Kamkar demonstrated a Wi-Fi based attack that allowed his device to intercept OnStar credentials from the RemoteLink mobile application—giving an attacker the ability to clone them and use them to track, unlock, and even remote start the vehicle. Kamkar discussed the details of the attack last Friday at DEF CON in Las Vegas, noting that the RemoteLink app on iOS devices had failed to properly check the certificate for a secure connection to OnStar’s server, or—as is more common in mobile apps using HTTPS to access Web services—use a “pinned” certificate hard-coded into the application itself. OnStar quickly resolved the issue with a RemoteLink app update.

But OwnStar has moved on to other targets. Today, Kamkar announced that he had adapted the tool to target applications for BMW Remote, Mercedes-Benz mbrace, and Chrysler’s Uconnect services on Apple iOS devices. All three, he said in an exchange with Ars via Twitter, have the exact same vulnerability as the RemoteLink app did: “no pinned cert or even PKI/[certificate authority] validation. Trivial to attack an unadulterated mobile device.”

The OwnStar device packs all the components required to execute this attack into a portable case that can be placed near a targeted vehicle. Like a virtual bear trap, it can capture the login credentials of a car owner using a mobile app to remotely unlock, lock, or start the vehicle, which can then be loaded onto a copy of the targeted mobile app on the attacker’s own device—giving the attacker the ability to execute all of the functions of the telematics system on the targeted vehicle. And it’s all because of a flaw that is all too common to mobile applications—reliance on a remote server’s certificate being valid, regardless of what network the connection is over.

Read 3 remaining paragraphs | Comments

Square will absorb its customers’ liability for fraud during EMV shift

On October 1, 2015, US commerce will undergo a considerable change—a variety of big credit card companies, financial groups, and issuers will require that merchants upgrade their point-of-sale (POS) terminals to accept chip-based cards as well as (and eventually, instead of) magnetic stripe cards. You may have already received chip-based replacements for your magnetic stripe cards in the mail.

The plan to transition to the new payment standard—called EMV for EuroPay, MasterCard, and Visa, (the developers of the standard)—was agreed upon in 2012, but a MasterCard press release circulated today cited a survey that said that 28 percent of small and medium business owners still aren’t aware of the new payment standard. That’s particularly troubling, because in the event of magnetic stripe card fraud at a store’s POS, the store will be liable for that faulty transaction if they don’t have up-to-date hardware that can accept chip cards. (Website-based transactions, commonly considered “card-not-present transactions,” are not part of the EMV transition and are treated separately.)

Today, payments processing company Square, founded by Twitter co-founder Jack Dorsey, said it wants to try to speed that adoption rate up in the next month or two, and hopefully convert some businesses to Square’s platform.

Read 4 remaining paragraphs | Comments

Report: Apple’s efforts to build a live-TV service have stalled

A report from Bloomberg today said that Apple is struggling to come to common ground with CBS, Fox, and Comcast-owned NBC in negotiations to offer a live TV streaming service much like Dish’s Sling TV.

The rumored service would be targeted at cord cutters, hosting a handful of live channels bundled together for about $30 to $40 a month. Back in March, the Wall Street Journal reported that Apple’s service would include networks like ABC, CBS, Fox, and various subsidiary channels like ESPN and FX. Apple has been pushing hard to develop a news and entertainment ecosystem to keep its users locked into its product line—earlier this year Apple announced a music streaming service and a curated news platform.

Although a September launch date—which would have coincided with the start of the new TV season—had originally been rumored for the service, Bloomberg‘s sources now say that live-TV streaming won’t hit the market until 2016. Besides the stalemate Apple has reached with CBS, Fox, and NBC, Bloomberg says that Apple decided to put a live-TV service on the back burner because it “doesn’t have the computer network capacity in place to ensure a good viewing experience.” Network capacity is a big deal for live-streaming—in Sling TV’s early days it struggled with the crush of customers demanding March Madness games.

Read 1 remaining paragraphs | Comments

Some stuff about things